
Visual SSL/TLS Certificate Manager
Never let an expired SSL certificate take your websites down. Issue free Let's Encrypt certificates in one click, verify auto-renewal timers, inject hardened Nginx/Apache HTTPS configs, and inspect cipher suites.
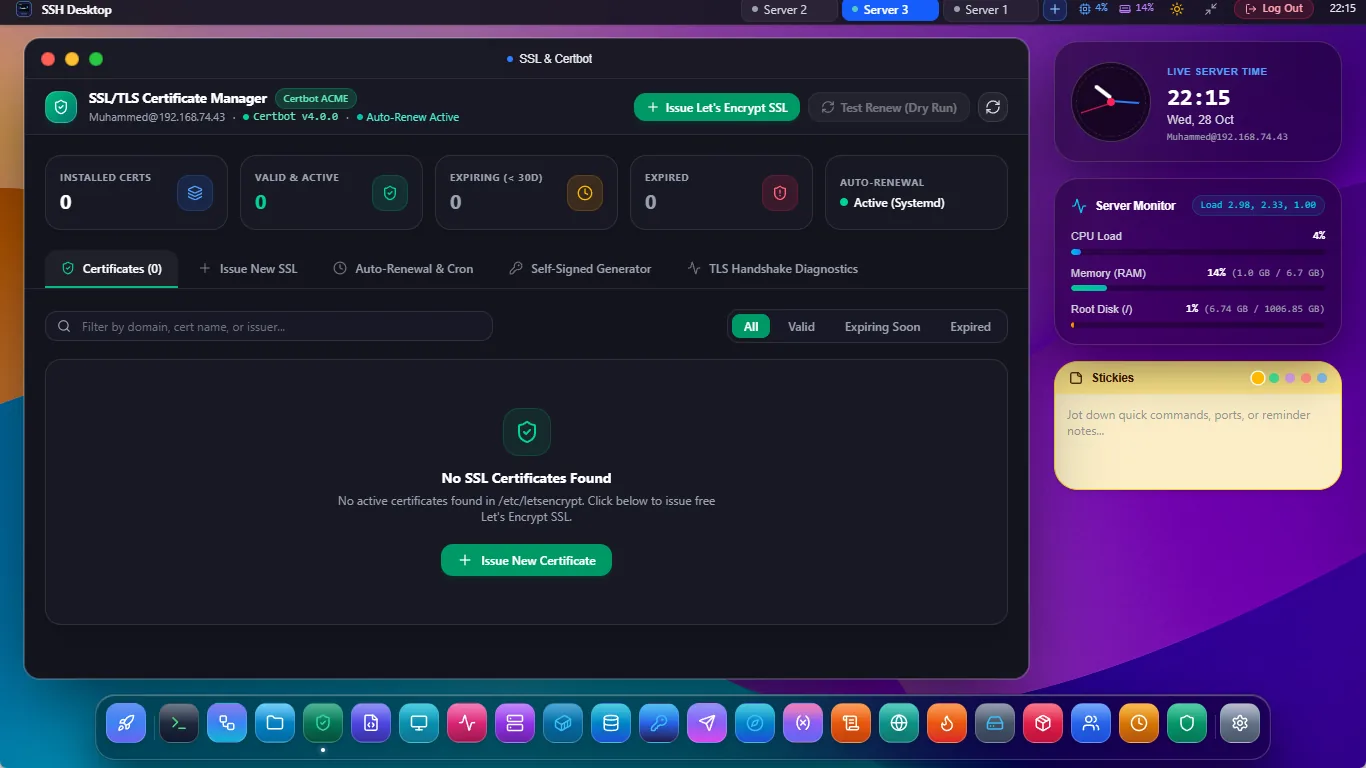
Zero-Friction HTTPS Deployment & Renewal
1-Click Let's Encrypt Issuance
Enter your domain names (e.g. api.example.com, example.com). SSH Desktop automatically completes HTTP-01 challenge verification and fetches production certs.
Expiration Countdown Gauges
Visual badges show remaining days until expiration. Alerts you in yellow at 30 days and red at 7 days, with automated dry-run testing for Certbot renewal daemons.
Hardened Nginx & Apache Configs
Injects industry-standard Mozilla Modern SSL configuration profiles featuring TLS 1.3 only, HSTS headers, OCSP Stapling, and ECDHE forward secrecy.
Supported ACME Validation Challenges
| Challenge Type | How It Works | Best For | Web Server Reload |
|---|---|---|---|
| HTTP-01 (Nginx/Apache) | Proves control by hosting an ephemeral token at /.well-known/acme-challenge/ |
Standard single-server web applications | Automated graceful reload (nginx -s reload) |
| HTTP-01 (Standalone) | Spins up an internal micro-server on port 80 to answer ACME challenge | Servers without active web servers yet | No prior web server configuration needed |
| DNS-01 (Wildcard) | Validates domain ownership via a DNS TXT record (_acme-challenge) |
Wildcard certs (*.domain.com) & private servers |
Cloudflare, Route53, DigitalOcean DNS API integration |
| Custom Keypair Upload | Allows manual upload of commercial EV/OV certificates (.crt + .key) | Corporate enterprise certificates | Validates private key modulus match before apply |
Frequently Asked Questions
What happens if port 80 is blocked by my hosting provider?
You can use the built-in DNS-01 challenge mode. SSH Desktop will display the exact TXT record name and value to add to your DNS provider, allowing SSL certificate issuance without needing port 80 open.
Can I force automatic HTTP to HTTPS redirect for visitors?
Yes. A single checkbox injects a 301 permanent redirect in your Nginx or Apache server block, redirecting all incoming HTTP traffic to HTTPS automatically.
Does it verify file permissions on private keys?
Yes. All generated and stored private keys (privkey.pem) are strictly locked to chmod 600 owned by root, preventing unauthorized read access by unprivileged users.
Secure All Your Domains with Zero Effort
Download SSH Desktop for Windows, macOS, or Linux. Free and open source with 25 built-in server administration tools.