
Visual Linux Network & Port Auditor
Instantly inspect every listening socket, active TCP connection, network adapter, and IP configuration. Identify rogue listeners, verify firewall exposures, and test DNS resolution without terminal friction.
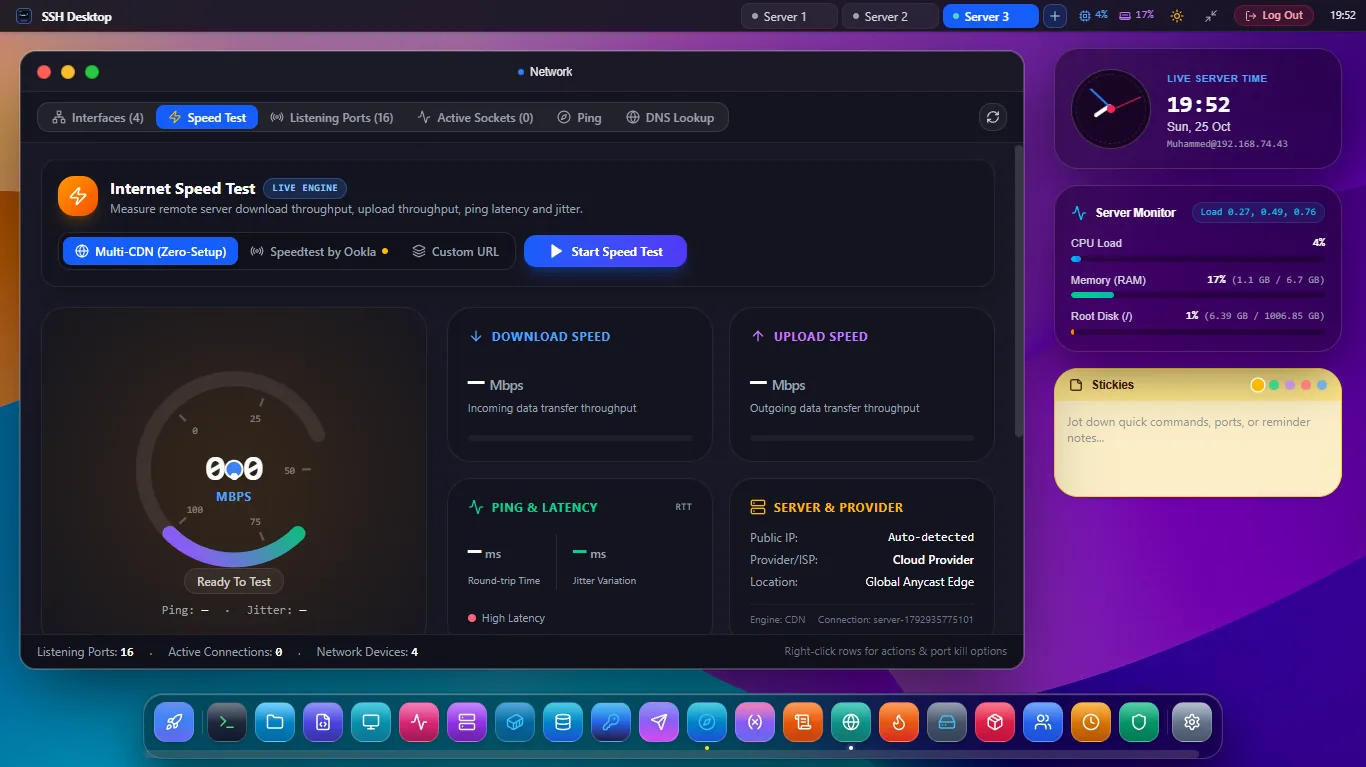
Deep Kernel Socket Inspection with ss & netstat
Listening Sockets Scanner
Parses Linux kernel socket structures (ss -tulpn) to reveal every process listening on TCP/UDP, distinguishing between private loopback (127.0.0.1) and world-accessible (0.0.0.0) bindings.
Interface Explorer
Inspect physical Ethernet (eth0), VPN virtual interfaces (wg0, tailscale0), and bridge adapters (docker0) with IP addresses, netmasks, MAC, and MTU values.
Built-in Network Diagnostics
Execute ICMP Ping tests with rolling latency graphs, Traceroute path hop inspectors, and DNS record queries (A, AAAA, CNAME, MX, TXT) straight from the server context.
Understanding Port Bindings & Security Exposure
| Binding Address | Exposure Level | Typical Safe Services | SSH Desktop Safety Tag |
|---|---|---|---|
| 127.0.0.1 / ::1 | Localhost Only | PostgreSQL, MySQL, Redis, internal reverse-proxy backends | Safe (Internal Loopback) |
| 0.0.0.0 / ::: | Publicly Exposed | SSH (22), HTTP (80), HTTPS (443) | Public (Verify Firewall Rules) |
| 10.x / 192.168.x / 172.x | Private Subnet | Internal cluster APIs, NFS, Kubernetes pod networks | LAN / Private Network |
| 100.64.0.0/10 (CGNAT) | Overlay Mesh | Tailscale, WireGuard, ZeroTier VPN nodes | Encrypted Mesh Tunnel |
Frequently Asked Questions
Can I jump from an open port to the firewall rule protecting it?
Yes! Clicking the "Firewall Action" button next to any listening socket opens App 8: Visual Firewall Manager with the port and protocol pre-filled, so you can block or restrict access in one click.
How often does the listening ports table refresh?
You can set auto-refresh to 1s, 5s, 10s, or manual trigger. Any new socket opened by an ephemeral process is highlighted with a pulse animation.
Does this tool support IPv6 sockets?
Yes. Both IPv4 and IPv6 sockets (e.g. :::80 or fe80::...) are fully parsed, formatted, and searchable.
Audit Your Server Network Surface Today
Download SSH Desktop for Windows, macOS, or Linux. Free and open source with 25 built-in server administration tools.