
Visual Linux Security Auditor & Hardening
Protect your servers against zero-day exploits, brute-force bots, and misconfigurations. Run automated CIS benchmark audits, verify SSH daemon hardening, scan SUID binaries, and track Fail2ban bans in real-time.
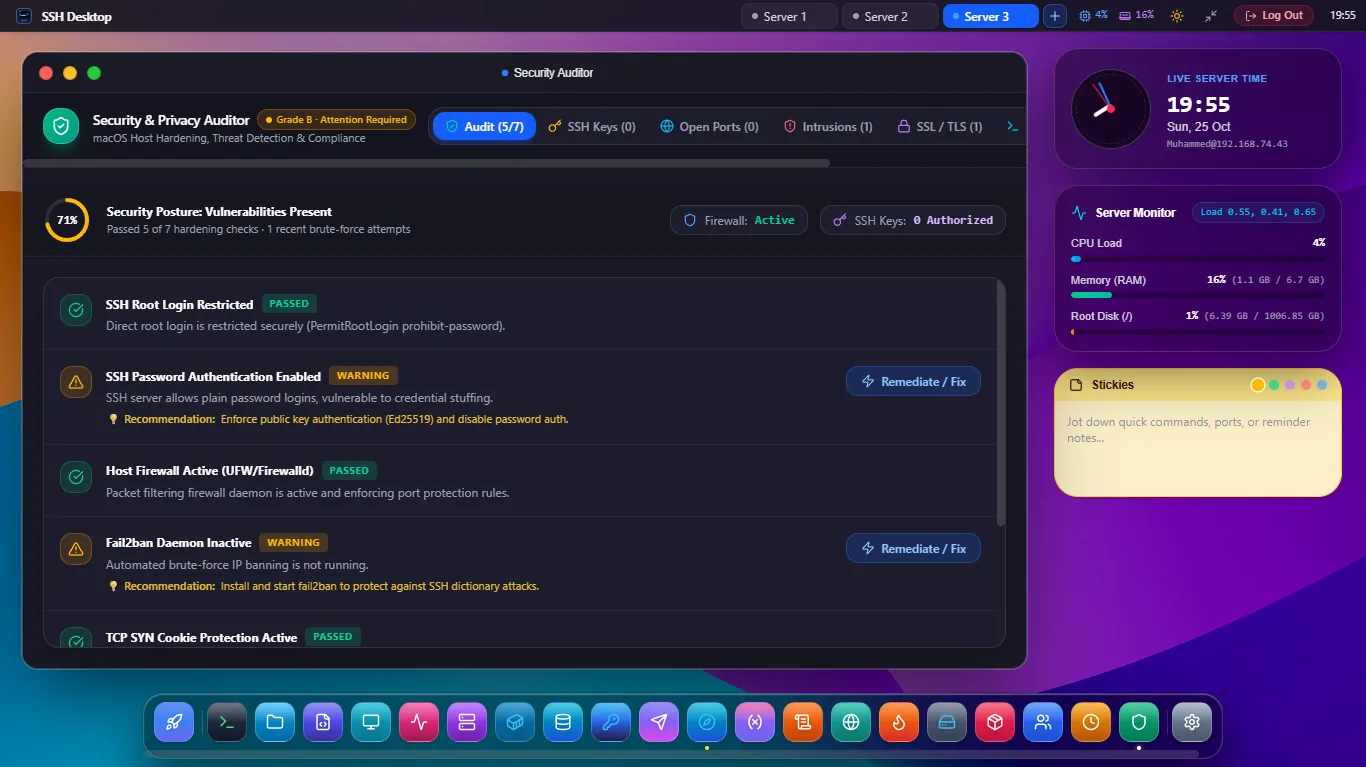
Automated Server Hardening & CIS Benchmarks
Hardening Index (0 - 100)
Runs a non-intrusive compliance audit inspired by Lynis and CIS benchmarks, providing an actionable score with color-coded high, medium, and low risk advisories.
SSH Daemon Hardening
Audits /etc/ssh/sshd_config for risky flags: enforces PermitRootLogin no, disables password authentication, restricts idle timeouts, and limits max authentication attempts.
Fail2ban & Brute-Force Jails
Monitors Fail2ban daemon status, showing real-time banned IP lists, failed authentication attempts, and unban controls across SSH, Nginx, and Postfix jails.
Critical Linux Server Hardening Vectors
| Security Vector | Standard Risk | Recommended Baseline | SSH Desktop 1-Click Fix |
|---|---|---|---|
| SSH Root Login | PermitRootLogin yes | PermitRootLogin no or prohibit-password |
Applies hardened directive and reloads sshd |
| Password Authentication | Vulnerable to brute force | PasswordAuthentication no (SSH Keys only) |
Verifies active key before disabling passwords |
| Firewall Status | Disabled (UFW/Iptables inactive) | Default deny incoming + allowed port 22/80/443 | Direct integration with App 8: Firewall GUI |
| SUID/SGID Binaries | Privilege escalation risk | Audit non-standard binaries outside /usr/bin | Flags unusual binaries for administrator review |
Frequently Asked Questions
Will hardening my SSH config lock me out of my server?
No! SSH Desktop includes a failsafe lockout prevention check: it validates that an SSH public key is already present in your authorized_keys and can authenticate before allowing you to disable password logins.
Does it detect unapplied security updates?
Yes. It links directly with App 11: Package Manager to flag critical pending CVE kernel and library patches.
Can I export a security audit report as PDF or Markdown?
Yes. You can export an executive summary or technical compliance report in Markdown or JSON format for compliance audits and SOC2/ISO27001 evidence.
Lock Down Your Linux Servers Today
Download SSH Desktop for Windows, macOS, or Linux. Free and open source with 25 built-in server administration tools.